
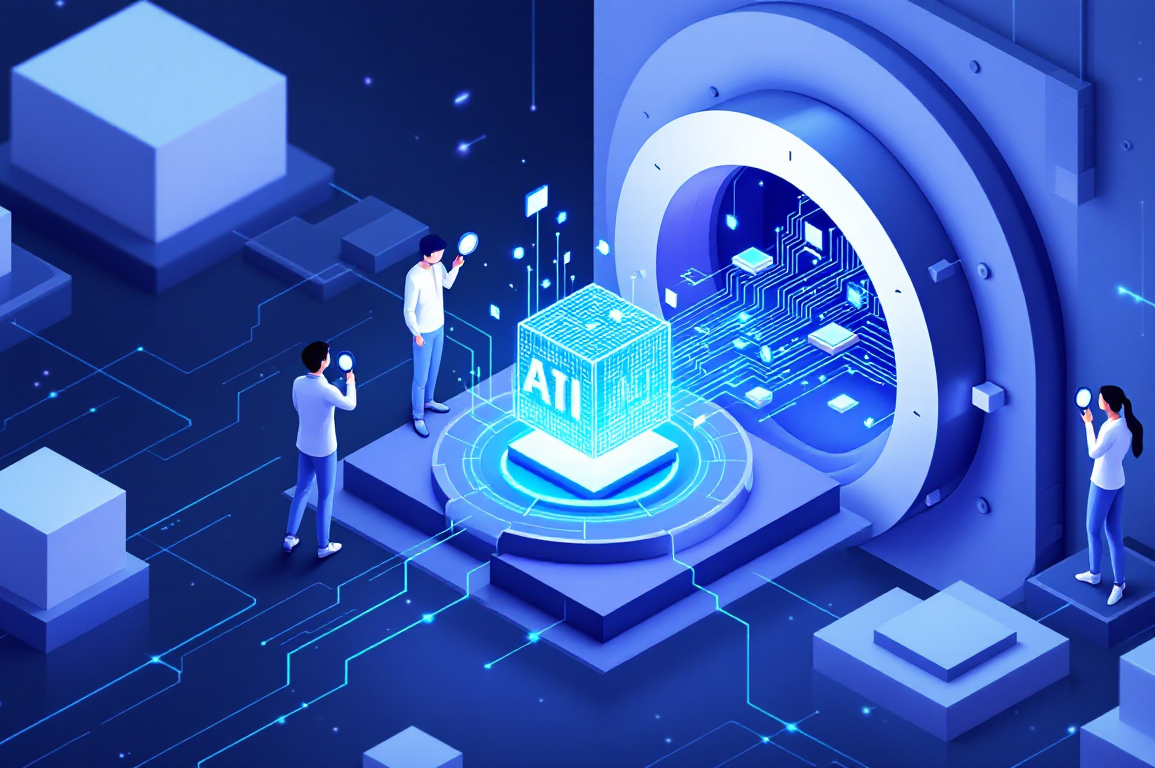

Anthropic has granted researchers from METR, an independent AI safety organisation, employee-level access to its systems and unrestricted publication rights, marking the first time a major AI laboratory has permitted such comprehensive external oversight of its models.
The arrangement, announced this week according to TechCrunch AI, allows METR researchers to conduct safety evaluations on Anthropic’s Claude models with the same level of system access granted to internal employees, whilst retaining full rights to publish findings without company approval or editorial control.
METR, formerly known as ARC Evals, specialises in evaluating AI systems for dangerous capabilities, including potential for autonomous replication, cyber-offensive operations, and deceptive behaviour. The organisation has previously conducted limited external audits for several AI laboratories, but typically under restrictive non-disclosure agreements that constrained both access depth and publication freedom.
The new framework represents a substantial departure from standard industry practice. Whilst companies including OpenAI, Google DeepMind, and Meta have permitted external researchers to evaluate their models, such arrangements typically involve controlled API access or time-limited testing environments, rather than direct system-level access comparable to internal security clearances.
According to the TechCrunch AI report, METR researchers will be able to examine Anthropic’s internal safety testing protocols, review training data governance, and conduct their own evaluations using the company’s computational infrastructure. Crucially, they retain discretion over what findings to publish and when, removing the editorial gatekeeping that has characterised previous third-party audit arrangements.
The business implications extend beyond Anthropic’s immediate competitive position. As regulatory frameworks for AI safety mature—particularly in the European Union under the AI Act and in California following recent legislative debates—the ability to demonstrate robust, independently verified safety practices may become a market differentiator and potentially a compliance requirement.
Companies that can credibly demonstrate transparent safety practices may gain preferential access to enterprise clients in regulated sectors such as healthcare, finance, and government services, where procurement increasingly demands documented third-party security validation. Conversely, laboratories unable or unwilling to permit comparable scrutiny may face market access constraints as corporate risk management standards evolve.
The arrangement also shifts competitive dynamics around safety talent. By allowing external researchers unfettered access, Anthropic effectively expands its safety research capacity without direct hiring costs, whilst potentially attracting collaboration from academics who might otherwise avoid industry entirely due to publication restrictions.
For METR, the partnership provides unprecedented research access that could yield publishable findings on frontier model capabilities and safety properties that have previously remained proprietary. This may establish METR as the de facto standard-setter for AI safety evaluation methodologies, particularly if other laboratories adopt similar access frameworks to maintain competitive parity on transparency.
The initiative arrives as AI laboratories face mounting pressure from researchers, policymakers, and civil society organisations to permit greater external scrutiny of safety claims. A coalition of over 200 AI researchers published an open letter in September calling for mandatory third-party auditing of frontier models, whilst the UK AI Safety Institute has sought—with mixed success—to negotiate evaluation access with major laboratories.
Whether competing laboratories will match Anthropic’s access framework remains uncertain. OpenAI has historically maintained tighter control over external evaluations, citing security concerns around model weights and training methods. Google DeepMind has permitted academic collaborations but typically under more restrictive terms than the METR arrangement.
The key indicator of this initiative’s broader impact will be whether other major laboratories announce comparable third-party access programmes within the next six months, and whether regulatory bodies begin citing independent evaluation access as a baseline expectation for frontier AI development. If adopted widely, such frameworks could fundamentally alter how AI safety claims are validated and how trust is established between laboratories, researchers, and the public.